Blockchain investigator ZachXBT shared on October 5 how he posed as a client to infiltrate a Chinese criminal network that he says laundered more than $1 billion in stolen crypto for North Korea’s Lazarus Group. The undercover operation followed the $1.5 billion Bybit hack in February 2025 and helped identify wallets moving stolen funds across several blockchains.
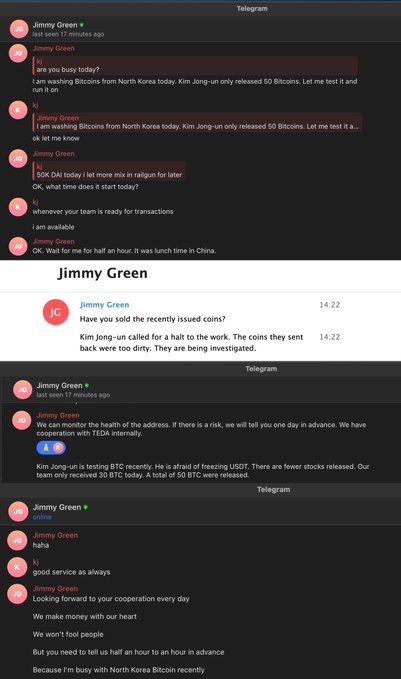
ZachXBT committed $349,700 to transactions with a Telegram user calling himself “Jimmy Green,” accepting a 5% loss on each trade to build trust. Green then shared details about the network’s operations in Hong Kong and mainland China, including planned transfers of Bybit proceeds before they happened.
Information from those conversations helped ZachXBT trace more than $12 million in Bybit hack funds. Tether later froze 442,000 USDT linked to the wallets he identified. The investigation also uncovered connections to Poloniex hack proceeds and $3 million in fraud-related funds traced to a Huione-linked wallet.
ZachXBT said he shared the findings with private-sector investigators and law enforcement working on the case. He waited until now to publish the investigation because of its sensitivity.
Public Support Requests Led to Jimmy Green
Following the $1.5 billion Bybit theft, attributed to the North Korea-linked hacking group TraderTraitor, ZachXBT noticed more than 15 accounts asking for help with crypto transfers and swaps in public Telegram and Discord groups. He linked those transactions to stolen Bybit funds and began contacting the users behind the requests.
Green was among those users. On March 6, 2025, ZachXBT funded a new Ethereum wallet to begin trading with him, exchanging USDC on Ethereum for USDT on Tron. Green’s receiving address obtained funds to pay transaction fees from a wallet ZachXBT traced to the Bybit theft and identified on the exchange’s public hack blacklist.
Repeated transactions and casual conversations built trust. Green began discussing upcoming movements of Bybit proceeds, including a planned transfer to Solana that ZachXBT observed the following day. Green claimed his team had laundered most of the stolen $1.5 billion, a claim ZachXBT said was consistent with the patterns he tracked.
On March 12, Green sent a screenshot of a cross-chain transfer. ZachXBT matched its amount and timing to a THORChain order created within minutes of the message, providing another link between the conversations and blockchain activity.
ZachXBT Traced Further Links to Poloniex, Huione, and Bitget
Three Solana addresses supplied by Green allowed ZachXBT to follow stolen funds moving between Bitcoin, Ethereum, Solana, and Tron in real time. He also identified laundering through Uniswap liquidity pools, where users deposit tokens to enable trading, involving tokens with little trading activity.
Green mentioned that a team he knew had funds frozen in 2024. ZachXBT traced that incident to 332,000 USDC stolen in the Poloniex hack. In a separate conversation, Green discussed laundering $3 million in fraud proceeds for another client. ZachXBT followed those funds to a wallet used by Huione Guarantee.
Similar activity continued after the $387 million Bitget hack in September 2026. On September 28, ZachXBT identified accounts publicly asking for help with transfers linked to that theft. He connected one of them to laundering proceeds from the $292 million Kelp DAO exploit earlier that year. Funds were moving between blockchains and into mixing services such as Wasabi, which make their origins harder to trace.
ZachXBT said his work has helped secure more than $75 million in freezes involving North Korean incidents since 2022, across multiple investigations. He asked for continued grants and donations to fund cases that require him to risk money and deal directly with criminal networks.